Customer Information: Cyber Resilience Act
To ensure the security of digital products in the EU, the EU has enacted the Cyber Resilience Act (CRA). The regulation applies to all products with digital elements, including software like our Digital Factory (DF). It mandates both processes and technical security requirements for manufacturers.
The Cyber Resilience Act (CRA) requires manufacturers to ensure the cybersecurity of their products throughout the entire lifecycle. This includes secure development, vulnerability handling, the provision of security updates, and the reporting of incidents to the authorities.
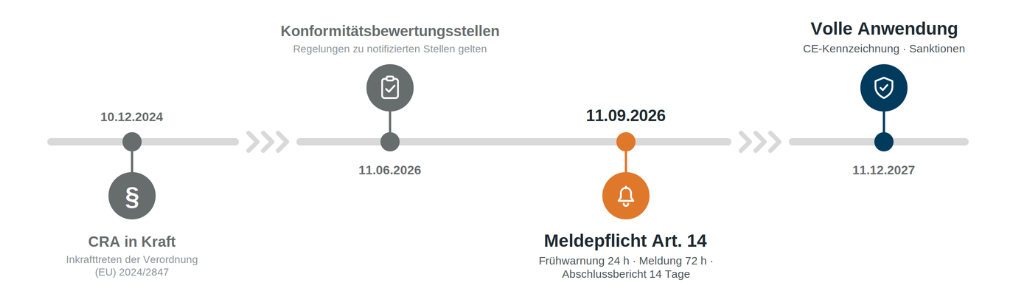
The CRA entered into force in December 2024. The first obligations apply from September 11, 2026, and full implementation is mandatory by December 11, 2027.
Autexis AG meets the requirements of the CRA that come into effect on September 11, 2026, and is implementing the additional requirements in stages through 2027. Our customers thus benefit from a regulated and transparent approach to hardware and software security.
What happens on September 11, 2026?
As of this date, the reporting obligation of the CRA (Art. 14) applies. If a vulnerability in our software is actively exploited or a serious security incident occurs, we must report this within specified deadlines to the EU reporting office, the ENISA Single Reporting Platform (SRP). In addition, we report such incidents voluntarily to the Swiss Federal Office for Cybersecurity (BACS). The reporting takes place in several stages:
Within 24 hours:
Early warning with vulnerability type and initial severity assessment
Within 72 hours:
Description of the vulnerability, method of exploitation, and action plan.
After 14 days or 1 month:
Final Report
What did Autexis AG do to achieve this?
Automated security audits of our software in development and operation.
A defined reporting process with established roles, duties, and escalation levels.
A single point of contact for security reports: security@autexis.ch. Vulnerabilities or suspected incidents can be reported to this address at any time.
Registration with the official reporting offices in the EU (ENISA) and Switzerland (BACS).
What does this mean for you as a customer?
Should a reportable incident affect your installation, we will inform you directly via your contact person. You will receive a description of the incident and, where possible, the recommended measures or a security update.
We regularly check the software versions deployed at your site against official vulnerability databases. This enables us to identify new vulnerabilities early, assess them, and initiate the necessary measures.
What are the next steps?
The CRA will become binding in stages, and the reporting obligation is the first step. By December 11, 2027, all requirements of the regulation must be met, including technical documentation, a product-specific risk analysis, and the provision of security updates throughout the entire support period.
Autexis AG is working on the implementation of these requirements and will inform you about the next stages.
If you have any questions, please contact your representative at Autexis AG or compliance@autexis.com.
